
13th Annual Rail Cybersecurity Summit
| Table | Topic | Discussion Lead(s) |
|---|---|---|
| RT1 | Resilient Rail: Keeping Mobility Moving in an Uncertain World Examining the shared responsibilities of manufacturers and operators for system-wide resilience. |
Eddy Thesee (Alstom) |
| RT2 | From NIS2 to IEC 63452: What Does Good Evidence of Rail Cyber Compliance Actually Look Like? | Joseph Mager (NS) & Bruno Corasolla (Hitachi Rail) |
| RT3 | Trusting Position: GPS Spoofing, PNT Resilience and Active Monitoring on the Connected Railway | Marc Silverwood & Gavin McAuley (Northern Trains) |
| RT4 | Autonomous AI Acceleration: What Should Rail Boards Be Governing Now? | Dimitri van Zantvliet (NS) |
| RT5 | Beyond Tier 1: How Far Down Your Digital Supply Chain Can You See? | Lead TBC |
| RT6 | Asset Visibility Across the Digital Railway: Do You Know What You Own & What Depends Upon It? | Lead TBC |
| RT7 | When Does Cyber Risk Become Safety Risk — and When Should It Enter the Safety Management System? | James Walker (ORR) |
| RT8 | Resilient Intelligence: What Happens When Connectivity, Data or the Application Cannot Be Trusted? | Lead TBC |
• Anatolii Protsiuk — Deputy Director for Corporate Security – Head of the Information Security and Personal Data Protection Division, JSC Ukrainian Railways (Ukrzaliznytsia)
• Oleksandr Rykovtsev — Director of Corporate Security, JSC Ukrainian Railways (Ukrzaliznytsia)
• Dimitri van Zantvliet — Director Digital Resilience / CISO, Nederlandse Spoorwegen (NS Rail)
• Dmitri Ivanov — Chief Information Security Officer, Eesti Raudtee (Estonian Railways)
• Independent Industry Moderator — TBC
| Table | Topic | Discussion Lead(s) |
|---|---|---|
| RT1 | Minimum Viable Company: What Absolutely Must Continue to Function After a Major Cyber Compromise? | Tom Remberg & Trond Eskild Tingstad-Stav (Bane NOR) |
| RT2 | Who Owns Cyber Risk After Fleet Handover? | Joshua Edgley (Hitachi Rail) |
| RT3 | Where OT Cybersecurity Breaks Down in Practice | Damanjit Singh (TfL) |
| RT4 | Keeping Safety Cases True Under Dynamic Cyber Risk | Jon Torode (RKH Qitarat) |
| RT5 | Cybersecurity by Design in Procurement: Setting Baseline Requirements Before the Contract Is Signed | Lead TBC |
| RT6 | Remote Access After Handover: Who Can Still Connect to the Train or Operational System? | Lead TBC |
| RT7 | Railway Security Information Sharing: Building Trusted Relationships Before a Crisis | Anatolii Protsiuk & Oleksandr Rykovtsev (Ukrainian Railways) |
| RT8 | From Cybersecurity Strategy to Delivery: What Works, What Doesn’t and What Have We Learned? | Salman Munir (Irish Rail) |
2027 Speakers

🇬🇧 James Walker
Head of Digital Safety, Railway Safety Directorate
Office of Rail and Road
🇫🇷 Eddy Thésée
Vice President, Products Cybersecurity
Alstom

🇩🇪 Dr. Frank Werner
Cybersecurity Expert
Eisenbahn-Bundesamt (NSA Germany)

🇳🇱 Joseph Mager
Manager Cyber Governance
Nederlandse Spoorwegen

🇳🇱 Dimitri van Zantvliet
Director Digital Resilience / CISO
Nederlandse Spoorwegen
🇬🇧 Marc Silverwood
Onboard Systems Manager
Northern Trains Limited
🇬🇧 Gavin McAuley
Onboard Systems Compliance Manager
Northern Trains Limited
🇳🇴 Tom Remberg
CISO
Bane NOR
🇳🇴 Trond Eskild Tingstad-Stav
Service Owner Traffic Operations
Bane NOR
🇬🇧 Joshua Edgley
Global Head of Fleet Security
Hitachi Rail
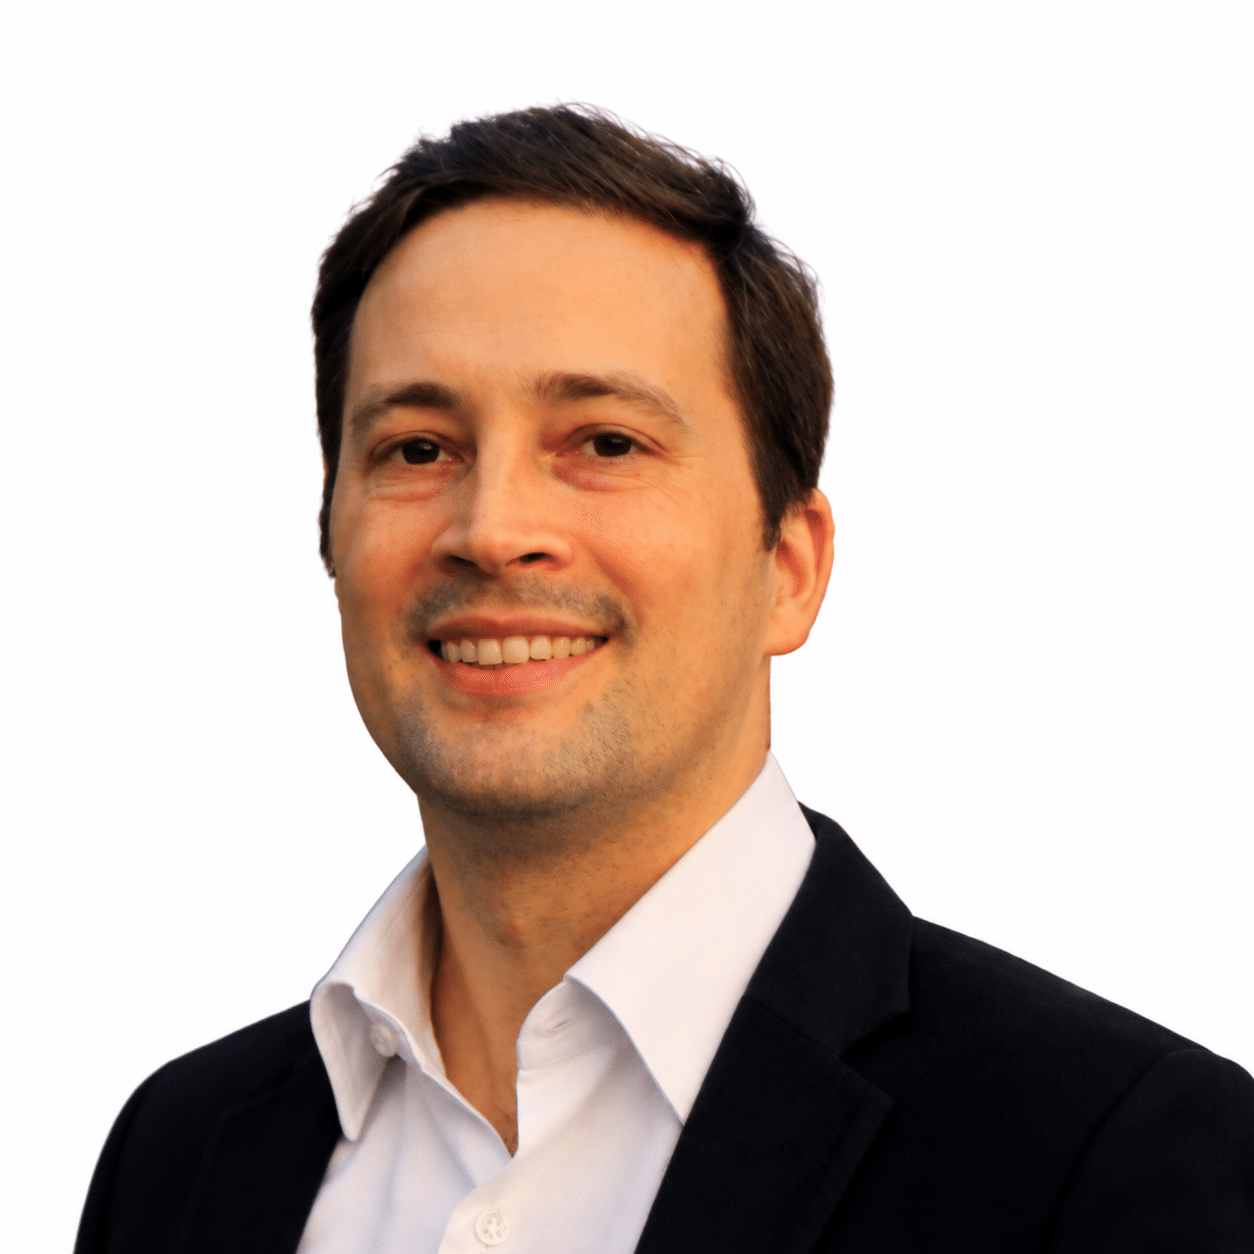
🇬🇧 Bruno Corasolla
Global Head of Digital Trains
Hitachi Rail
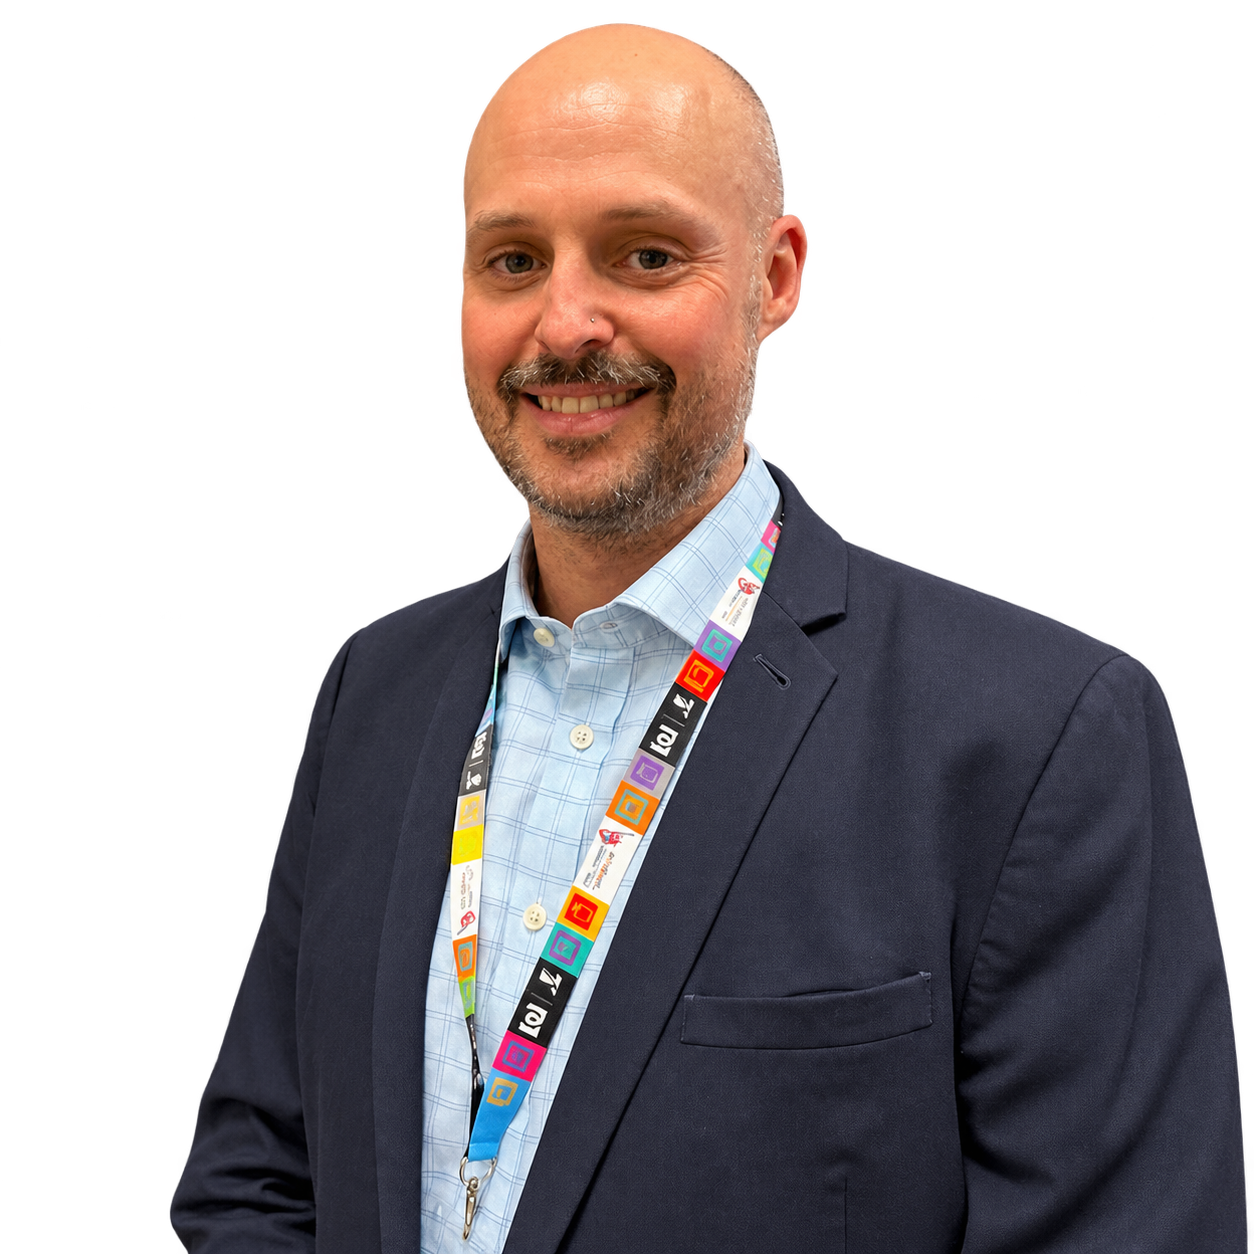
🇶🇦 Jon Torode
Head of Engineering and Asset Performance
RKH Qitarat
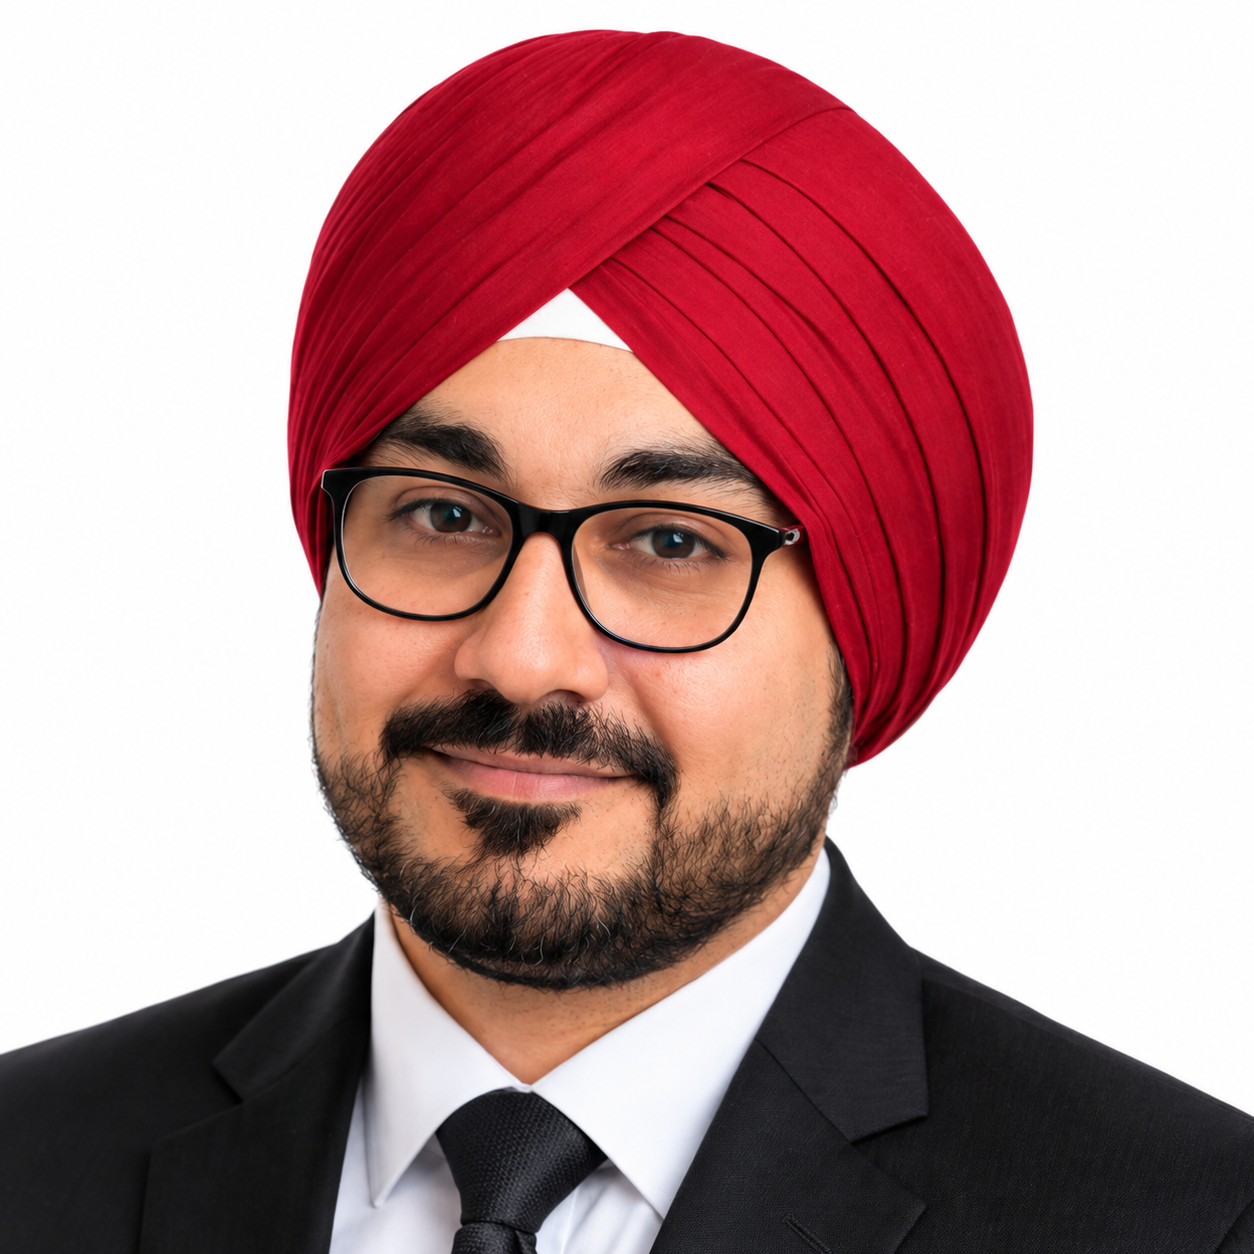
🇬🇧 Damanjit Singh
Cyber Security Engineer (Signal Operations & Maintenance)
Transport for London
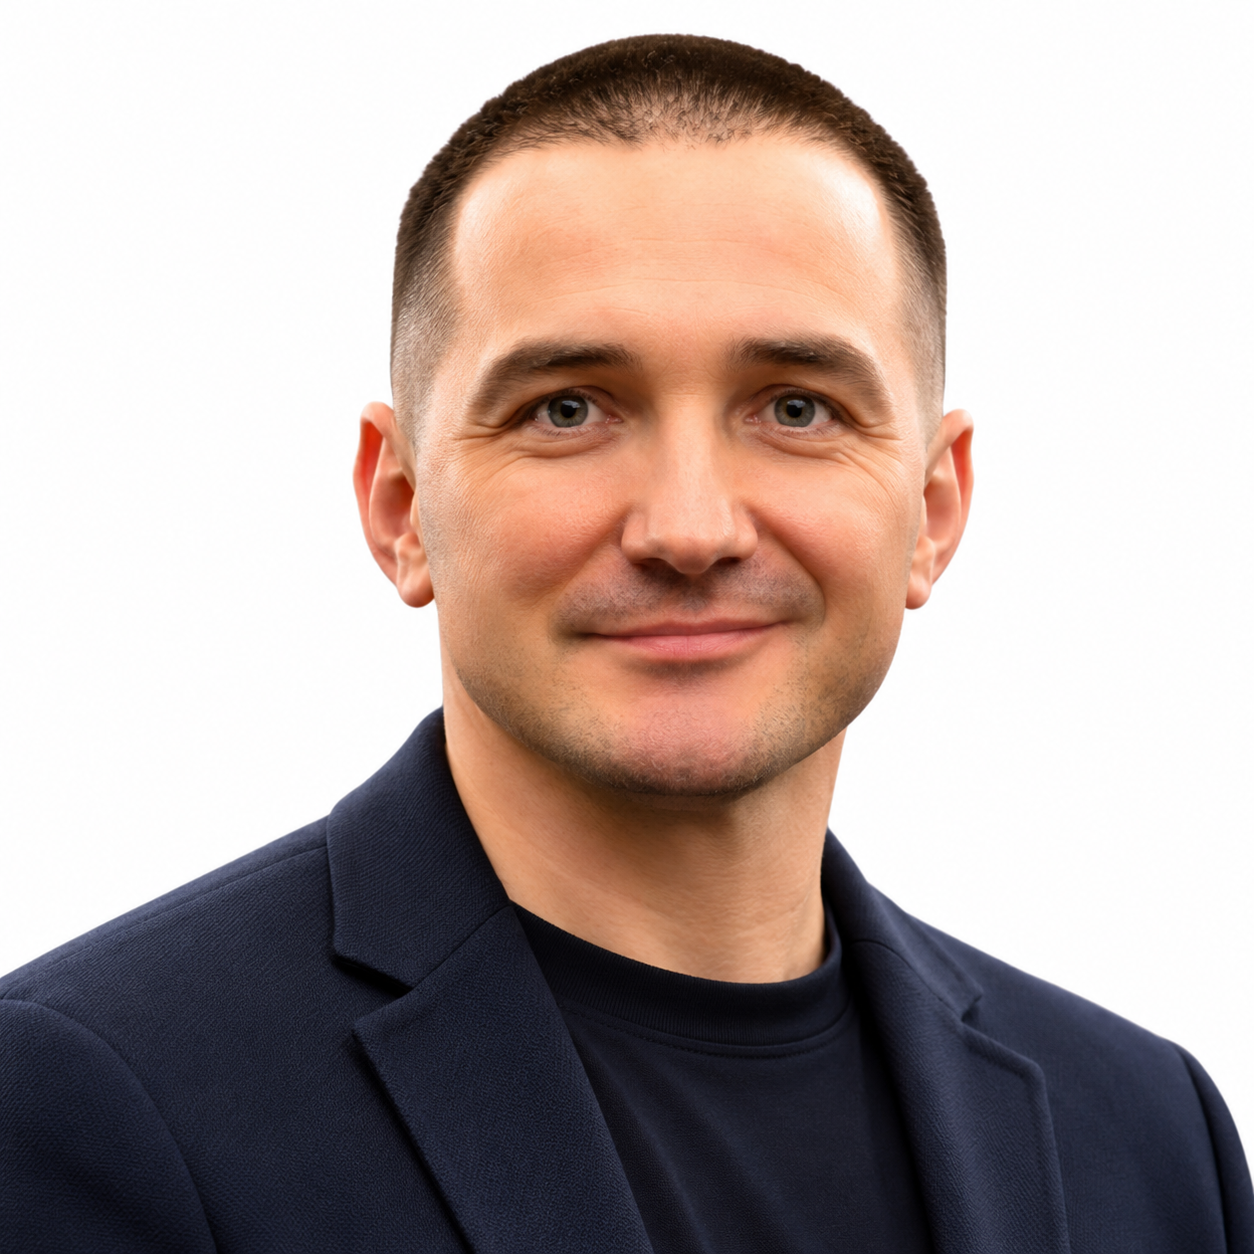
🇮🇪 Salman Munir
OT Cyber Security Manager
Iarnród Éireann
🇪🇪 Dmitri Ivanov
Chief Information Security Officer
AS Eesti Raudtee / Estonian Railways Ltd
🇬🇧 Mark Robinson
Chief Information Officer
DfT Operator
🇺🇦 Oleksandr Rykovtsev
Director of Corporate Security
JSC Ukrainian Railways (Ukrzaliznytsia)
2027 Sponsors
Sponsors
Sponsors

Exhibitor

Near Capacity for 2027. Register while places remain 📢
Sponsorship | Speaking | Workshops | Attending
Contact: [email protected]
Past Attendees Include 👥
Rail Cybersecurity brings together the organisations that operate, own, engineer, assure and secure railway systems, alongside the specialist technology and cybersecurity companies supporting them.
Rail & Transit Operators / Infrastructure
- Abellio
- ADIF
- Angel Trains
- Arriva
- ARTC
- Austrian Railways
- Bane NOR
- Banedanmark
- BLS
- Calgary Transit
- Central Japan Railway Company
- CFL
- Chiltern Railways
- CN Rail
- Crossrail
- CSX
- DB Cargo
- DB Cargo UK
- DB InfraGO / DB Netz
- DB Regio
- DB Schenker
- DB Systel
- DB Systemtechnik
- Deutsche Bahn
- Direct Rail Services
- East Midlands Railway
- East West Rail
- Eversholt Rail
- Fintraffic
- Flix
- GB Railfreight
- Govia Thameslink Railway
- Great Western Railway
- Heathrow Express
- HS1
- HS2
- Irish Rail / Iarnród Éireann
- Land Transport Authority Singapore
- LNER
- London Northwestern Railway
- Metropolitan Transportation Authority (MTA)
- Metro Service Copenhagen
- Network Rail
- Network Rail Telecom
- Northern
- NS / Dutch Railways
- Porterbrook
- RKH Qitarat
- Rock Rail
- SBB Swiss Federal Railways
- SNCF
- SNCFL
- South Western Railway
- Sporveien
- STIB-MIVB
- Strathclyde Partnership for Transport
- The Copenhagen Metro
- Toronto Transit Commission
- Trafikverket
- TransPennine Express
- Transport for London
- Transport for Wales
- Transport UK Group
- West Midlands Trains
- YPTO
Rolling Stock, Signalling & Rail Technology
- Alstom
- Belden
- CAF
- CAF Signalling
- Camlin Rail
- DeltaRail
- duagon
- Egis Rail
- EKE-Electronics
- ENYSE
- Euro-Multitel
- Frauscher Sensortechnik
- HARTING
- Hitachi Rail
- Hit Rail
- Icomera
- IMH Technologies
- Knorr-Bremse
- Kontron Transportation
- Loram
- Nomad Digital
- OMICRON electronics
- Patentes Talgo
- Perpetuum
- Power Standards Lab
- Resonate Group
- Schweitzer Engineering Laboratories
- Selectron Systems
- Siemens Mobility
- Stadler Rail
- Telent
- Televic Rail
- Thales
- Turntide
- Westermo
Cybersecurity & OT Technology
- 4Secure
- Acalvio Technologies
- aDolus Technology
- Airbus CyberSecurity
- AM Cyber
- Ampere Industrial Security
- Applied Risk
- Auxilium Cyber Security
- Auxilium Pentest Labs
- BlackBerry
- Cervello
- Codewerk
- Comcast DataBee
- Complete Cyber
- Computacenter
- Context Information Security
- Cyber Innovation Hub
- Cyber Shield
- Cyberics
- Cygnia Technologies
- Cylance
- Cylus
- Cyolo
- DigiTribe
- Dragos
- Expandium
- Fortinet
- GDAK Cyber Solution
- Huawei Technologies
- Huld
- Hypasec
- IBM
- iHackLabs
- IL7 Security
- Industrial Defender
- Information Security Forum
- Irdeto Security
- Mandiant
- mnemonic
- Modux
- NCC Group
- Nozomi Networks
- OTORIO
- Palo Alto Networks
- Pen Test Partners
- RazorSecure
- Risk Ledger
- SecurityScorecard
- Shift5
- Stoïk
- WALLIX
- Waterfall Security Solutions
- Xage Security
- XONA Systems
Engineering, Consulting & Assurance
- Abbott Risk Consulting
- Adelard
- Amentum
- Aon
- Arcadis
- Arup
- AtkinsRéalis
- Bird & Bird
- Bureau Veritas
- Deloitte
- DNV
- Egis
- Expleo Group
- Frazer-Nash Consultancy
- HNTB
- Ineco
- NCB Rail Assurance
- Network Certification Body
- PA Consulting
- PROSE
- SYSTRA
- TÜV Rheinland
- VUZ
- WSP
Government, Regulators, Standards & Academia
- British Transport Police
- Cyber Security Agency of Singapore
- Danish Transport and Construction Agency
- Department for Transport
- DfTO
- Eisenbahn-Bundesamt
- ERTMS Users Group
- European Commission – DG CONNECT
- European Commission – DG MOVE
- European Union Agency for Railways
- Finnish Transport and Communications Agency
- Human Environment and Transport Inspectorate
- NCSC
- NCSC Netherlands
- Nuclear Decommissioning Authority
- Office of Rail and Road
- Rail Delivery Group
- Rail Safety and Standards Board
- Shift2Rail Joint Undertaking
- Traficom
- University of Birmingham
- University of Huddersfield
- University of Warwick
Additional Organisations Represented
- Aspen Insurance
- Hiscox
- Honda
- MAPNA
- Mondi Group
- Petroleum Development Oman
- Solventum
Past attendee organisations are shown to demonstrate the breadth of the Rail Cybersecurity community and do not imply participation in the 2027 event. Company names have been consolidated where the same organisation has attended under different subsidiaries or legal entities.
Get in touch
Enquire About Rail Cybersecurity 2027
Register your interest in speaking, sponsorship, exhibition or attending the next Rail Cybersecurity Summit.
Join the Rail Cybersecurity Summit WhatsApp Group

News
Technology drives innovation in Buildings Post COVID19
What will the buildings sector look like post coronavirus? How can we utilise innovation to ensure business continuity and better define resilience? As the sector looks at how post-COVID19 digital retrofits will be implemented and financed, now is the time for the C Suite to not lose sight of the fundamentals of cybersecurity by design. New technology deployments will need to be more secure than ever and getting C level buy-in will be paramount.
Selecting and Safely Using Collaboration Services for Telework
Selecting and Safely Using Collaboration Services for Telework.
During a global pandemic or other crisis contingency scenarios, many United States Government (USG) personnel must operate from home while continuing to perform critical national functions and support continuity of government services. With limited access to government-furnished equipment (GFE) such as laptops and secure smartphones, the use of (not typically approved) commercial collaboration services on personal devices for limited government official use becomes necessary and unavoidable.
Cyber Senate launches new Directors Clubs post Coronavirus lockdown
Cyber Senate today announced the launch of the Directors Clubs©, that will commence once lockdown has ended and the government give the all-clear for a minimum of twenty people to meet at any one time in the UK, Europe and North America.
Risk Management for Novel Coronavirus (COVID-19)
This product is for executives to help them think through physical, supply chain, and cybersecurity issues that may arise from the spread of Novel Coronavirus, or COVID-19. According to the U.S. Centers for Disease Control and Prevention (CDC), COVID-19 has been detected in locations around the world, including multiple areas throughout the U.S. This is a rapidly evolving situation and for more information, visit the CDC’s COVID-19 Situation Summary
https://www.cisa.gov/publication/cisa-insights-publications
“Cyberattack on the nation’s critical infrastructure and economic system would create chaos “
“A major cyberattack on the nation’s critical infrastructure and economic system would create chaos and lasting damage exceeding that wreaked by fires in California, floods in the Midwest, and hurricanes in the Southeast.” As stated in the Chairman’s Opening Letter in a new report from the Cyberspace Solarium Commission. “Our country is at risk, not only from a catastrophic cyberattack but from millions of daily intrusions disrupting everything from financial transactions to the inner workings of our electoral system. Capturing the complexity of this challenge is hard.”
Rail Cyber Security Post Event Report
During February 18th-19th Westlands Advisory attended the Cyber Senate on Rail Industry Cyber Security. The event was attended by executives and management from Train Operating Companies (TOC), Rolling Stock and Signalling Manufacturers, Cyber Security Engineers and Consultants, and Technology vendors. The presentations, panel discussions and debate during networking breaks covered issues ranging from implementation of standards to managing challenges such as third-party risk and developing defence in depth.
Innovation and change are coming to the rail industry. As infrastructure projects approach the end of lifecycles, a new era of rail travel is emerging that will be defined by digital technology, enabling improved services and better experiences. A digital rail network also brings security challenges that need to be addressed to ensure that the rail industry maintains its impressive safety record. Whilst security and safety are not inextricably linked, a security failure may have an adverse effect on rail industry safety, and this has resulted in a considerable amount of work to establish security standards and controls to improve cyber resilience.
To purchase this in depth review of the state of the industry, please visit https://cybersenate.com/rail-cyber-security-report/0dtxb5m8cxc5hxe1bs9fos8gihsjcc


